The Asymmetric Battlefield of Modern Cybersecurity
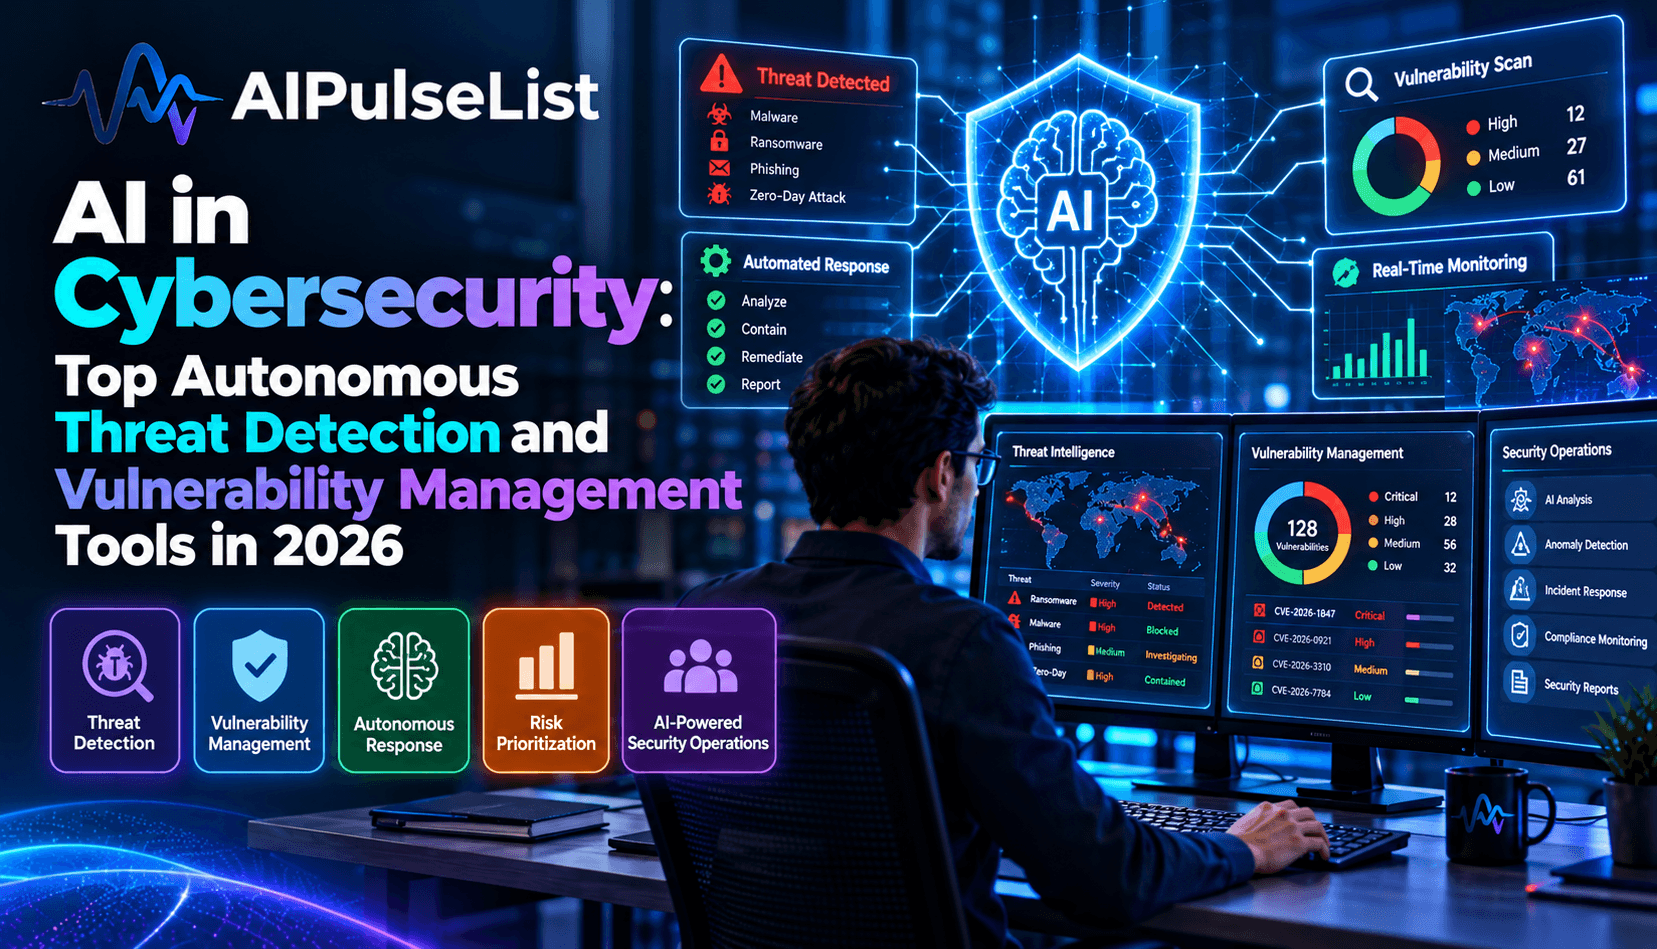
The cybersecurity landscape in 2026 is defined by unprecedented machine-speed asymmetry. Gone are the days when malicious actors were limited to manual vulnerability scanning, misspelled Nigerian prince phishing emails, and off-the-shelf malware scripts. Today, cybercrime syndicates and state-sponsored Advanced Persistent Threats (APTs) deploy autonomous AI agents capable of generating context-perfect spear-phishing payloads, synthesizing deepfake executive voice authorizations, and autonomously probing enterprise firewalls for zero-day vulnerabilities in real time.
Faced with an onslaught of thousands of synthetic attacks per hour, human Security Operations Center (SOC) analysts are severely outmatched. Manual alert triage leads to acute analyst burnout and dangerous alert fatigue—allowing critical intrusions to dwell undetected for months inside corporate networks.
To defend against machine-speed attacks, enterprises must deploy machine-speed defenses. Modern AI-driven cybersecurity platforms do not rely on outdated static signature databases; they leverage self-learning behavioral analytics, automated threat hunting copilots, and autonomous containment protocols that isolate compromised endpoints in milliseconds before data exfiltration can occur.
💡 Pro-Tip for SecOps Professionals:
Explore verified defensive software in our Cybersecurity & Safety AI Directory to compare threat intelligence platforms, zero-trust agents, and compliance audit tools.
The Core Pillars of AI-Powered Defense
Modern defensive security systems integrate machine learning across four critical defensive layers:
- Behavioral Anomaly Detection (Self-Learning Immune Systems): Rather than looking for known malware fingerprints, the AI models normal user, device, and network traffic patterns. When an employee credential suddenly downloads 50 gigabytes of database records at 3:00 AM from an unfamiliar IP address, it is flagged as an active anomaly regardless of whether malware signatures are present.
- Autonomous Micro-Containment: In the event of a high-confidence ransomware outbreak, the defensive agent isolates the infected workstation from the internal local area network in under 200 milliseconds, terminating malicious processes before lateral movement spreads across the server fleet.
- Generative SOC Copilots: Transforming complex SIEM logs, raw hex dumps, and multi-cloud telemetry into concise human-readable incident narratives, recommending specific remediation steps for junior analysts.
- Continuous Automated Red-Teaming (CART): Simulating real-world adversary tactics, techniques, and procedures (TTPs) 24/7 against your own cloud perimeter to uncover exposed S3 buckets, outdated SSL certificates, and misconfigured API endpoints before external hackers exploit them.
1. Darktrace / Immune System: Self-Learning Cyber AI
Darktrace remains the technological benchmark for autonomous, self-learning network defense. Founded by mathematical researchers from the University of Cambridge and government intelligence experts, Darktrace does not rely on prior assumptions about what attacks look like.
Standout Strengths:
- Enterprise Immune System: Learns the "pattern of life" for every device, user, and cloud resource across Microsoft 365, AWS, Salesforce, and industrial OT networks.
- Darktrace Antigena (Autonomous Response): When anomalous lateral movements or unauthorized data encryptions occur, Antigena takes surgical, proportional actions—blocking the anomalous connection without interrupting legitimate business operations.
- Cyber AI Analyst: Reduces investigation time by 92% by autonomously stitching together disparate alert crumbs into a single unified forensic root-cause timeline.
2. CrowdStrike Charlotte AI & Falcon Next-Gen SIEM
CrowdStrike is an undisputed titan of endpoint detection and response (EDR). With its generative security engine, Charlotte AI, CrowdStrike combines petabytes of real-time threat intelligence with conversational natural language execution.
Standout Strengths:
- Natural Language Threat Hunting: Tier-1 analysts can ask questions like: "Are any hosts in our AWS production cluster communicating with known Russian command-and-control servers?" and receive verified lists of impacted endpoints with immediate remediation buttons.
- Identity Threat Protection: Detects credential stuffing and adversary Kerberoasting attempts by continuously analyzing Active Directory telemetry and anomalous token usage.
- World-Class Threat Graph: Collects trillions of security events daily from across the globe, ensuring that an attack detected in Tokyo instantly immunizes endpoints in London and New York.
3. SentinelOne Singularity AI
SentinelOne built its platform on a foundational philosophy: on-device autonomous intelligence. Unlike cloud-dependent solutions that suffer latency delays when processing petabytes of raw logs, SentinelOne executes behavioral AI models directly at the endpoint kernel level.
Standout Strengths:
- Offline Protection: Even if a laptop is completely disconnected from the internet, the local behavioral model detects and terminates ransomware instantly.
- 1-Click Automated Rollback: In the catastrophic event that ransomware alters or encrypts local files, SentinelOne leverages Windows Volume Shadow Copies and proprietary journaling to restore every encrypted file back to its pristine state in one click.
- Purple AI Analyst: An interactive AI assistant that accelerates threat hunting queries, autonomously drafts formal post-incident breach reports for legal counsel, and maps indicators against the MITRE ATT&CK framework.
Platform Comparison Matrix for Enterprise CISOs
| Security Solution | Primary Specialty | Autonomous Action Speed | Deployment Surface | Key Differentiator |
|---|---|---|---|---|
| Darktrace | Network Behavioral Immune Defense | Under 1 second | Network, Cloud, Email, OT/IoT | Zero rules or training required |
| CrowdStrike Charlotte | Endpoint Telemetry & Threat Intel | Near real-time (Cloud broker) | Endpoints, Cloud Workloads, Identity | Vast global adversary threat graph |
| SentinelOne Singularity | On-Device Autonomous Containment | Sub-millisecond (Kernel level) | Windows, macOS, Linux, Kubernetes | 1-Click Ransomware Rollback |
Case Study: Neutralizing a Multi-Vector Ransomware Incursion in 400 Milliseconds
To grasp the difference between traditional manual alarm systems and autonomous AI defense, consider a live incident recorded at a major Midwestern logistics provider in early 2026. An employee in accounts payable opened an encrypted PDF invoice containing a polymorphic payload designed to bypass standard antivirus signatures.
Upon execution, the malware spawned an unauthorized PowerShell process attempting to dump LSASS memory credentials and locate internal network file shares for encryption:
- Millisecond 0–120: The on-device behavioral model detected anomalous process memory injection and unauthorized shadow copy deletion commands.
- Millisecond 120–250: The agent severed network adapters on the host machine via software-defined firewalls, preventing the malware from establishing an external command-and-control connection.
- Millisecond 250–400: The malicious process tree was killed, and journaled disk snapshots reverted two encrypted metadata files to their original state.
- Millisecond 400+: The SOC team received a fully synthesized forensic report detailing the infected email source, compromised hashes, and proof of zero lateral impact.
Essential SecOps Implementation Checklist for 2026
To ensure your organization is equipped to survive modern autonomous cyber threats, implement these strategic milestones:
- Mandate Multi-Factor Authentication with FIDO2 Hardware Keys: AI voice and video deepfakes can easily bypass SMS and email verification codes. Hardware security keys (YubiKeys) provide mathematical immunity against credential phishing.
- Deploy Behavioral Email Ingestion Filters: Replace standard static MX-record spam filters with computer vision and natural language models that inspect incoming email links in isolated cloud sandboxes before delivery.
- Enforce Zero-Trust Network Architecture (ZTNA): Terminate perimeter-based VPN access. Verify identity, device compliance, and behavioral risk scores on every single micro-request.
- Conduct Regular AI Deepfake Defense Drills: Train executive assistants and finance personnel to never execute out-of-band wire transfers based on voice calls or video conferences without pre-agreed in-person verification protocols.
Conclusion: The Machine Fights the Machine
Cybersecurity is no longer a human versus human conflict; it is an algorithmic contest fought between malicious automated bots and defensive artificial intelligence systems. By equipping your defensive operations with self-learning behavioral analytics and autonomous containment capabilities, you level the playing field—ensuring that your organization's critical assets remain resilient in an era of relentless technological warfare.